Traceable test scope
Connect targets, roles, objectives, and approvals to each assessment.
Security assurance
DeepScan supports evidence for SOC 2, ISO 27001, HIPAA, and customer assurance reviews by preserving scope, activity, findings, remediation, and retest history.
The operating gap
Auditors and customers need clear evidence of what was tested, what was found, how risk was handled, and whether corrective action was verified.
Capabilities
One evidence trail from test to assurance.
Connect targets, roles, objectives, and approvals to each assessment.
Preserve reproducible proof and business impact instead of unverified alerts.
Keep ownership, guidance, and status attached to the original evidence.
Retest corrected paths and retain the result for review.
Workflow
One approved objective. One record.
Document targets, objectives, credentials, and operating boundaries.
Execute controlled testing with a complete activity record.
Give owners validated evidence and practical guidance.
Retest fixes and package the history for assurance review.
Evidence
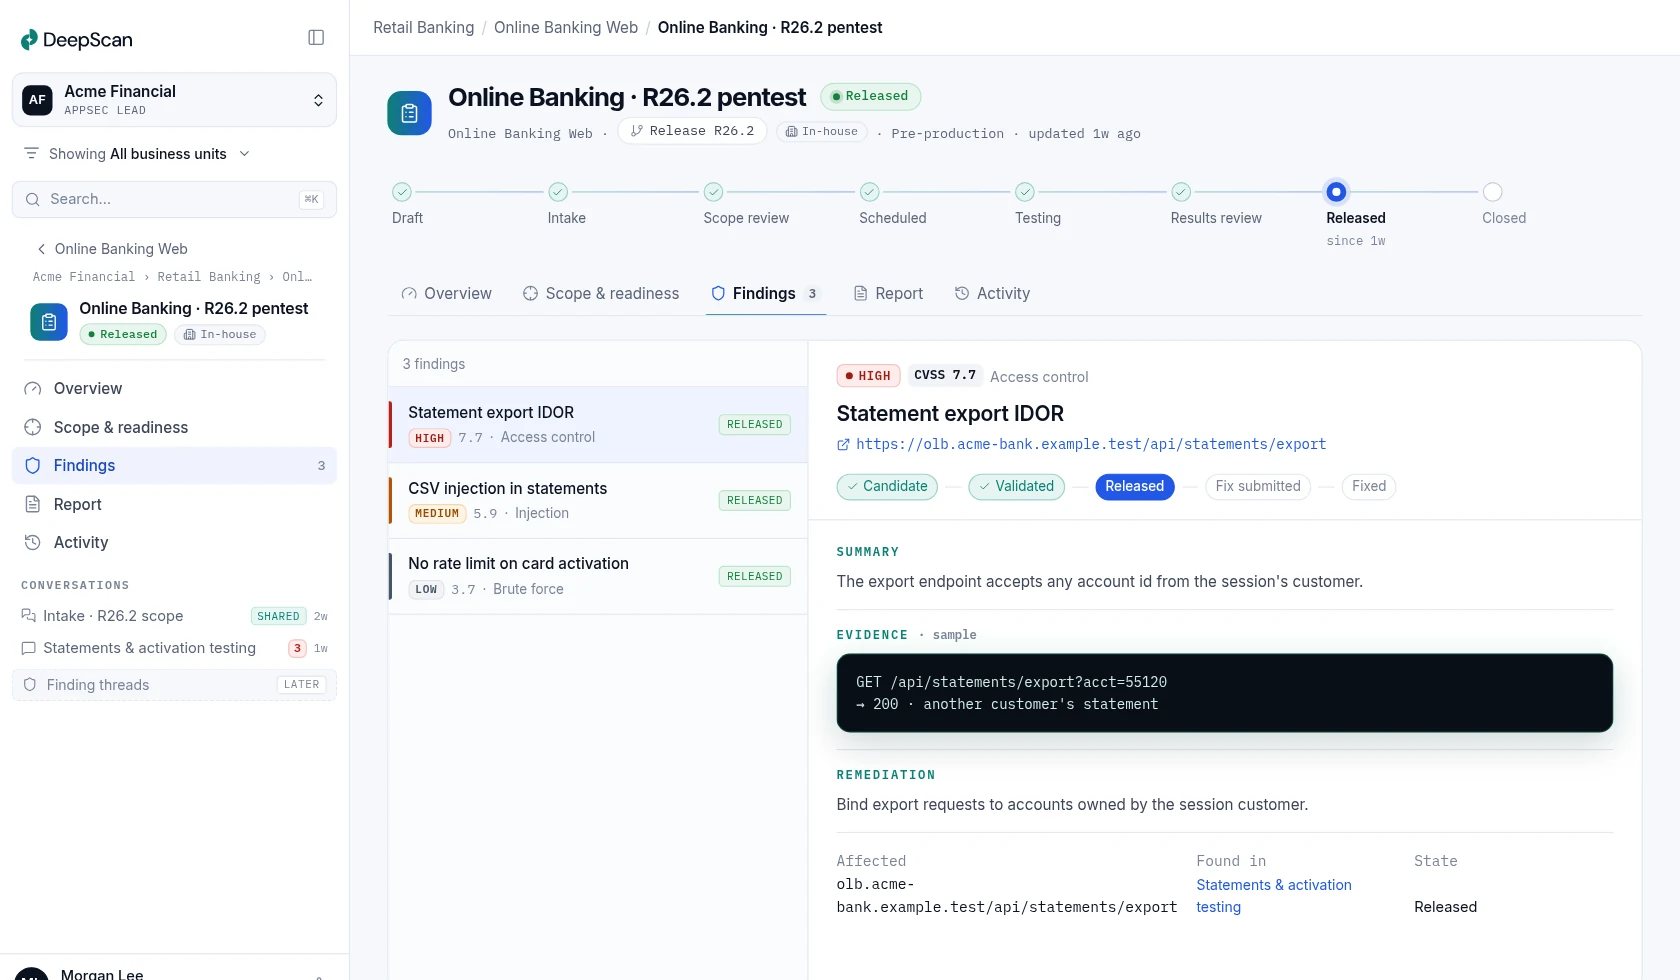
Technical depth for testers. Clear outcomes for leaders.
Governance and safety
Define where DeepScan can operate, how it validates, and who reviews the evidence.
Questions
Practical answers about scope, delivery, evidence, and ownership.
No. DeepScan provides security-testing evidence that can support assurance activities; certification decisions remain with the relevant auditor or assessor.
Evidence may support SOC 2, ISO 27001, HIPAA, customer security reviews, and other assurance workflows depending on your controls and assessor requirements.
Yes. When a formal report is required, DeepScan expert-led pentests are delivered through CyberImmune, a CREST Pathway Company.
Start with proof
Start with an approved target.