Agentic pentesting for AppSec
Clear the pentest queue.
App teams request. Agents prepare and test. Your AppSec team approves and releases.
- Requesters
- AppSec team
- Vendors
- One engagement
deepscan · scope & readiness
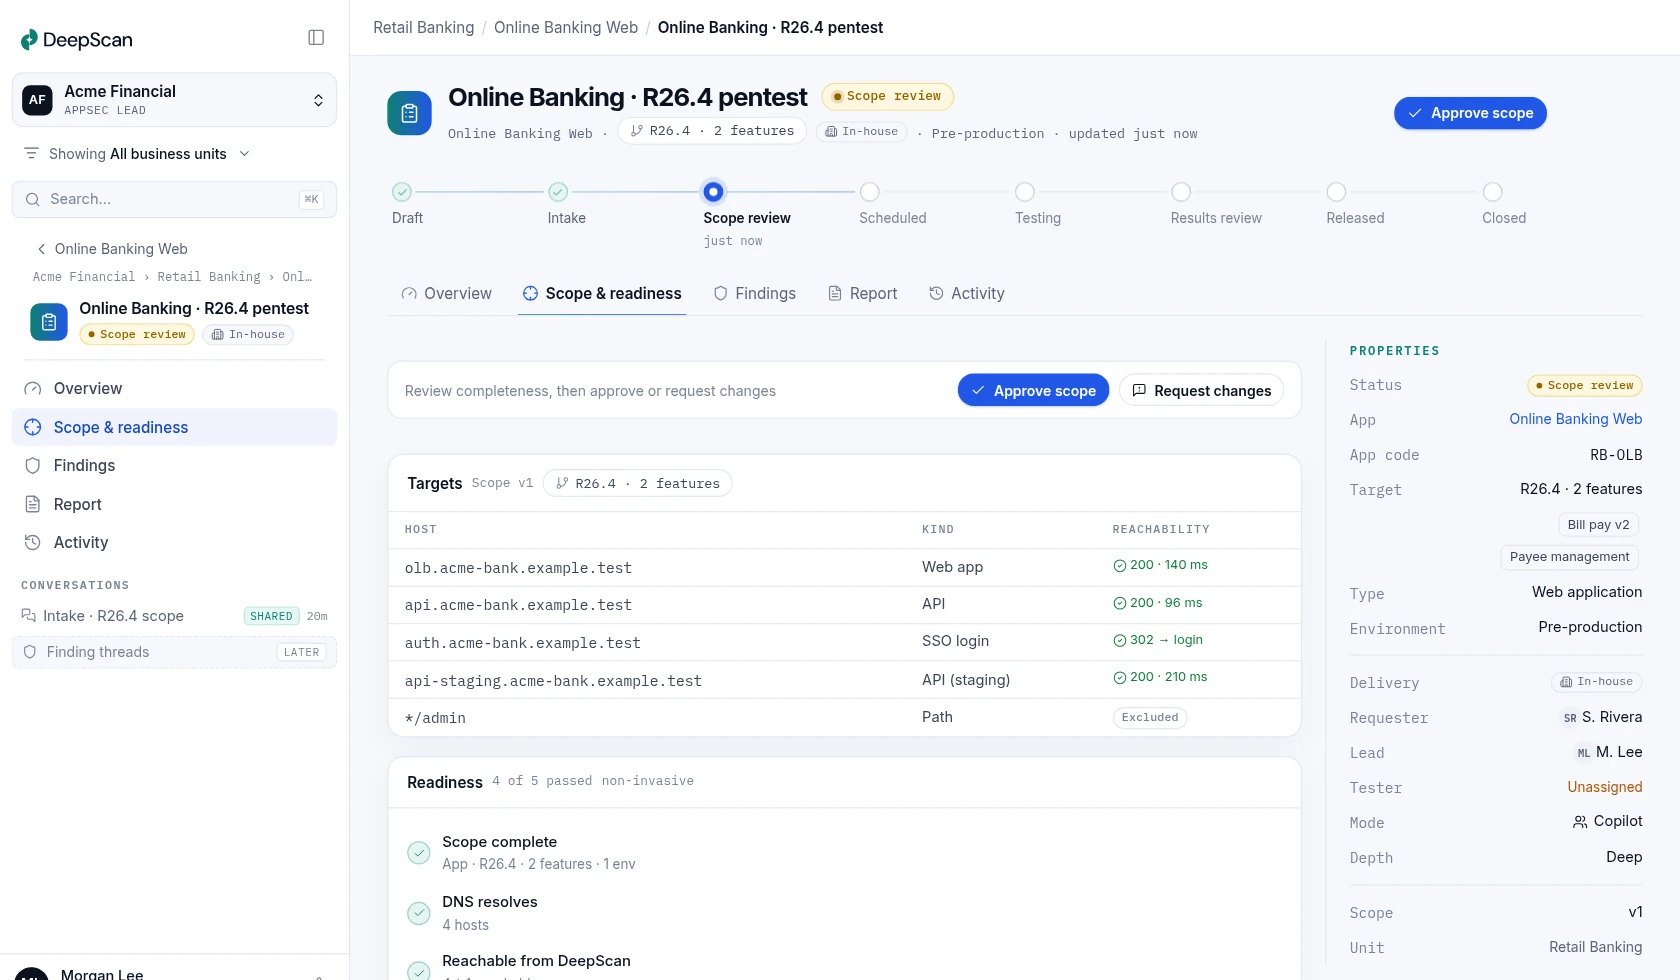
Engagement lifecycle
Requesters, AppSec and vendors. One engagement.
Every request, scope decision, test, finding and retest lives in one record.
- Draft
- Intake
- Scope review
- Scheduled
- Testing
- Results review
- Released
- Closed
RequesterApp teams ask once.
AppSec teamAppSec stays in control.
- Approve scope
- Assign or hand off
- Release
Pentester or vendorTesters work in context.
- Autonomous
- Copilot
- Validate
Preparation
Agents prepare every pentest for AppSec.
Agents work with app teams on scope and access. AppSec approves.
- 01
Scoping agent + application teamGather testing context
Collect targets, roles, access, and testing rules from the application team.
- 02
Validation agentResolve scope and access gaps
Flag missing context or invalid credentials for the application team to resolve.
- 03
Readiness recon agentConfirm readiness
Check reachability and basic navigation without attack activity.
- 04
AppSec handoffApprove active testing
AppSec reviews the prepared engagement and authorizes testing.
Execution
Autonomous execution. Expert direction.
Agents test. Your pentesters direct and validate.
- Explore authenticated workflows and trust boundaries
- Investigate authorization, business logic, and connected attack paths
- Validate exploitability and capture evidence
AppSec pentester
Pentesters direct and extend
- Add application context and testing priorities
- Introduce hypotheses and steer investigations
- Deepen validation and assess impact
AppSec workspace
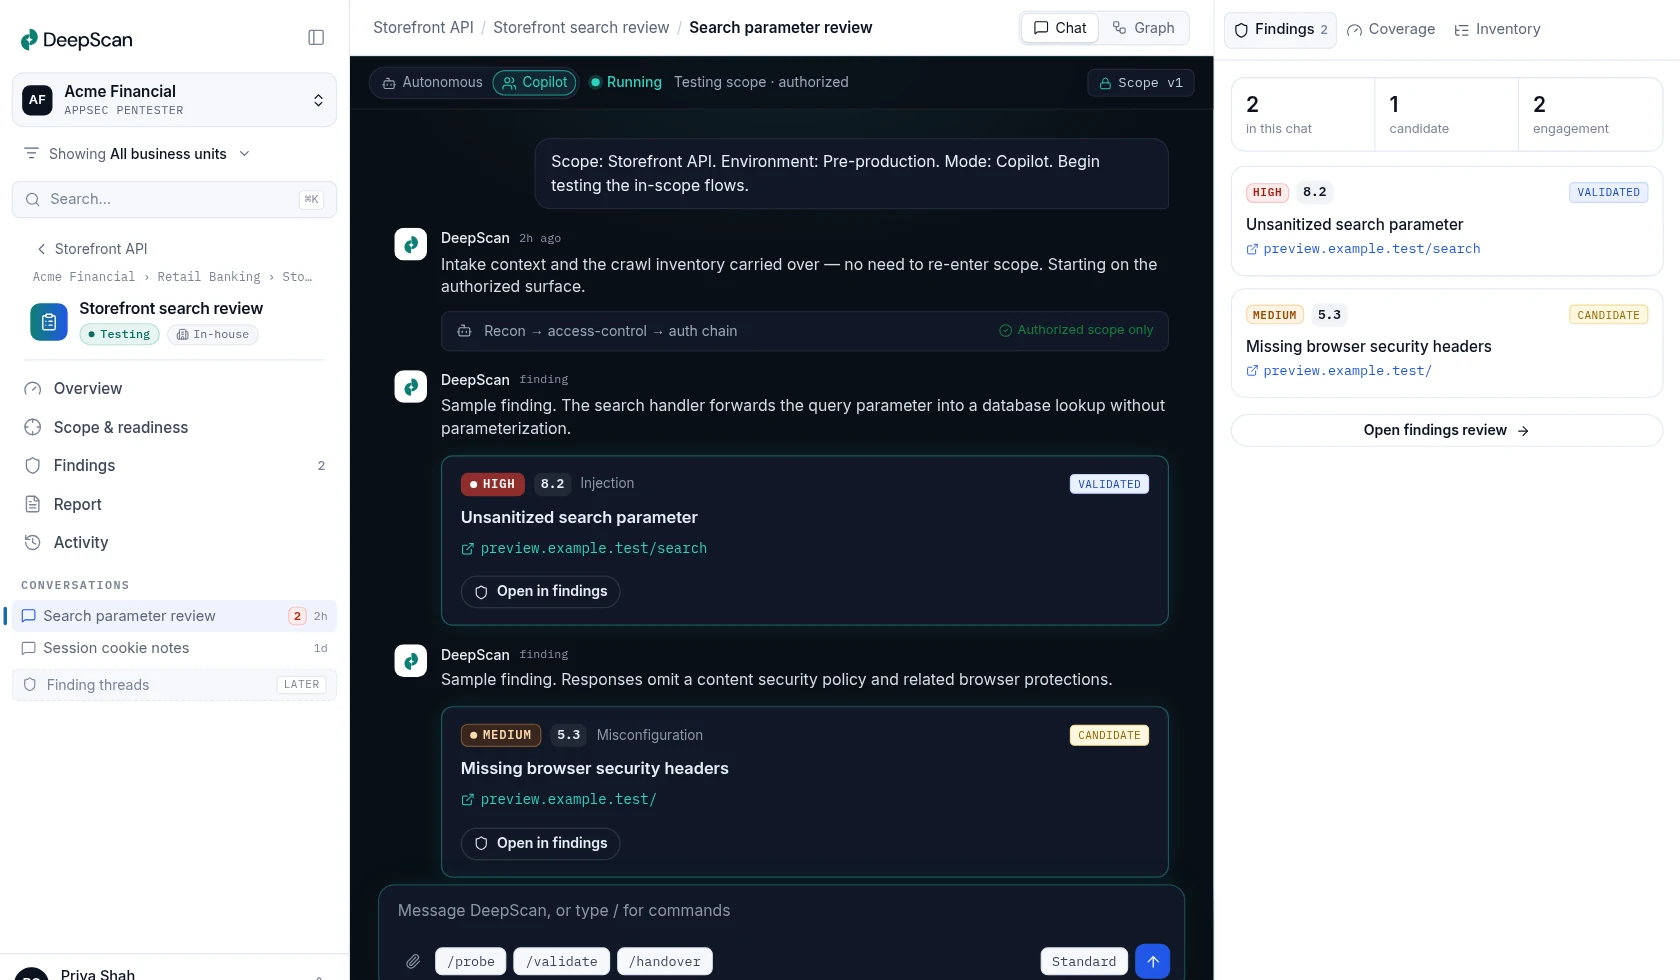
Inside an application pentest.
Direct the next test and confirm findings in one chat.
deepscan · testing chat
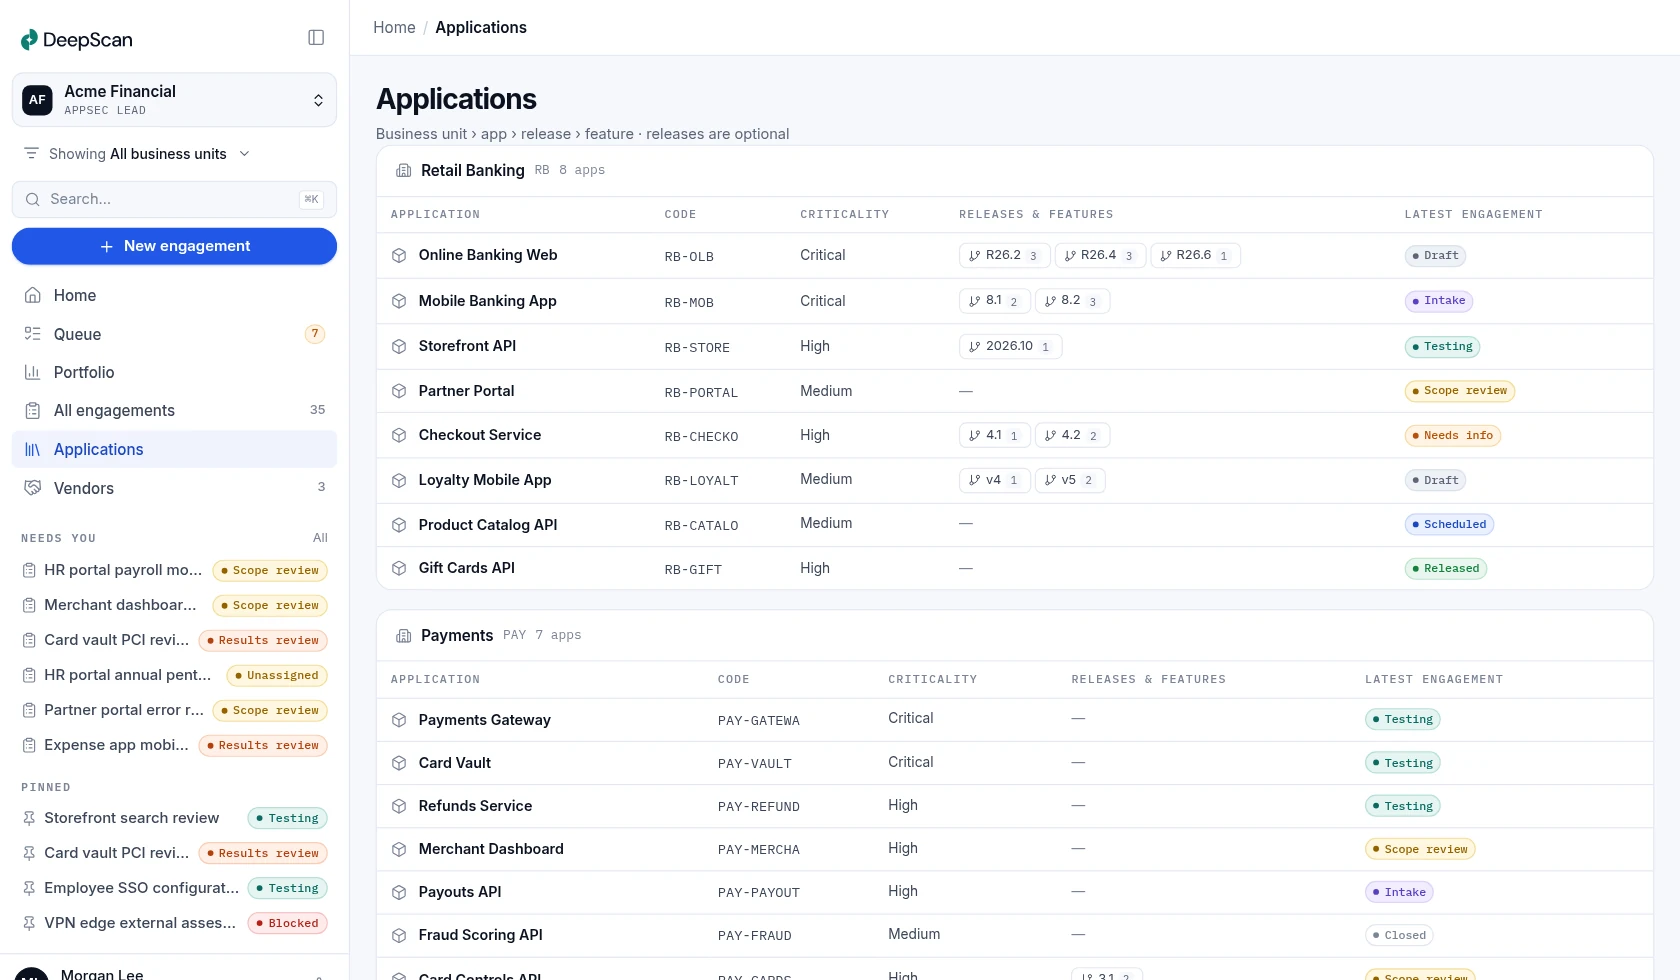
Portfolio operations
Operate several pentests at once.
Every app, release and engagement state in one catalog.
deepscan · applications
Release control
Your team decides what leaves the workspace.
Assign in-house or hand off to a vendor. AppSec releases results and tracks retest.
01Validate
02Review
03Release
04Remediate
05Retest
Release urgent findings while testing continues.
Start with proof
Bring your next application.
From request to released findings and retest.