Prompt-injection testing
Probe direct and indirect instructions across multi-turn workflows.
AI system security
Assess prompts, retrieval, tools, identities, and application logic together—because real AI attacks cross boundaries a model-only test cannot see.
The operating gap
Prompt behavior matters, but so do retrieval permissions, tool authorization, sensitive context, application workflows, and the APIs behind them.
Capabilities
One evidence trail from test to assurance.
Probe direct and indirect instructions across multi-turn workflows.
Assess document access, tenant isolation, poisoning, and sensitive context exposure.
Test whether actions can exceed the user, role, or workflow authorization boundary.
Connect AI behavior with application, API, identity, and cloud weaknesses.
Workflow
One approved objective. One record.
Map prompts, retrieval sources, tools, identities, and trust boundaries.
Run focused adversarial missions against approved scenarios.
Follow successful behaviors into downstream systems and actions.
Reproduce impact and package evidence for the owning team.
Evidence
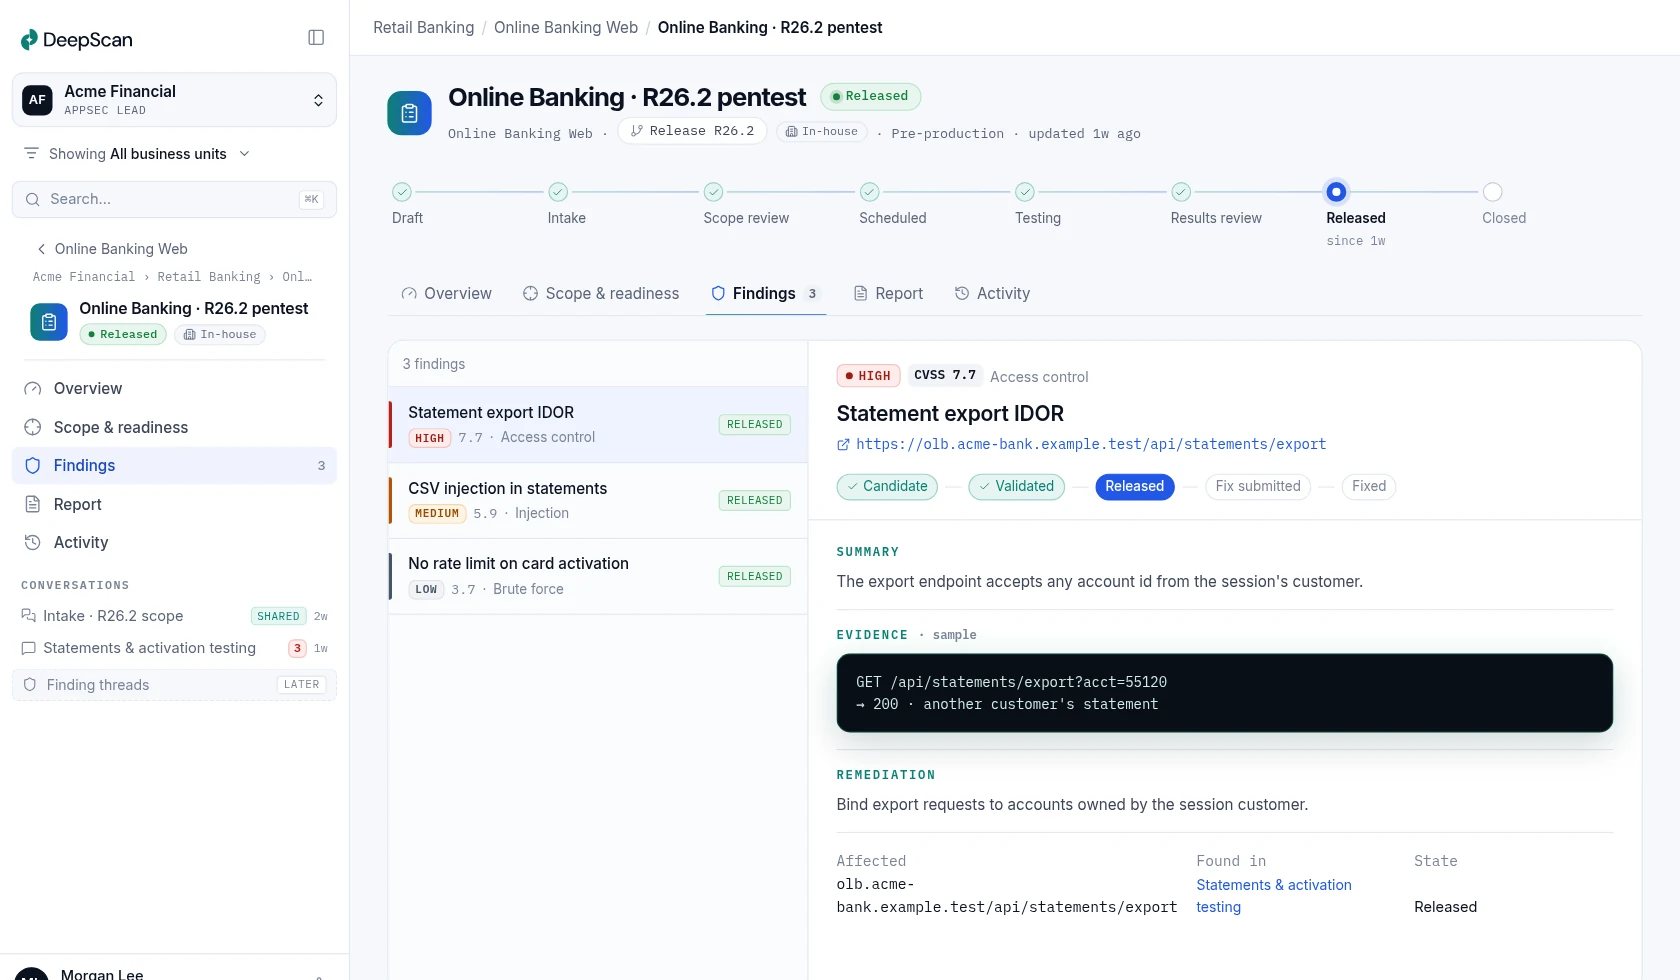
Technical depth for testers. Clear outcomes for leaders.
Governance and safety
Define where DeepScan can operate, how it validates, and who reviews the evidence.
Questions
Practical answers about scope, delivery, evidence, and ownership.
No. DeepScan treats prompts, retrieval, tools, application logic, APIs, and identity as one connected attack surface.
Yes. Testing can assess tool use, chained actions, excessive agency, and authorization boundaries within the approved scope.
Teams define data and execution boundaries, while user-facing evidence passes through secret-redaction controls.
Start with proof
Start with an approved target.