Adversary emulation
Turn approved objectives into repeatable attack scenarios across supported surfaces.
Built for offensive teams
Agents run approved attack paths. Your operators steer in Copilot.
Red Team capacity
Run more approved objectives with shared attack context and operator control.
Turn approved objectives into repeatable attack scenarios across supported surfaces.
Reproduce weaknesses and establish the impact of an attack path.
Follow multi-step workflows, state changes, and trust boundaries.
Test privileges, ownership, and access across identity and tenant boundaries.
Test prompt injection, retrieval boundaries, and unsafe tool use.
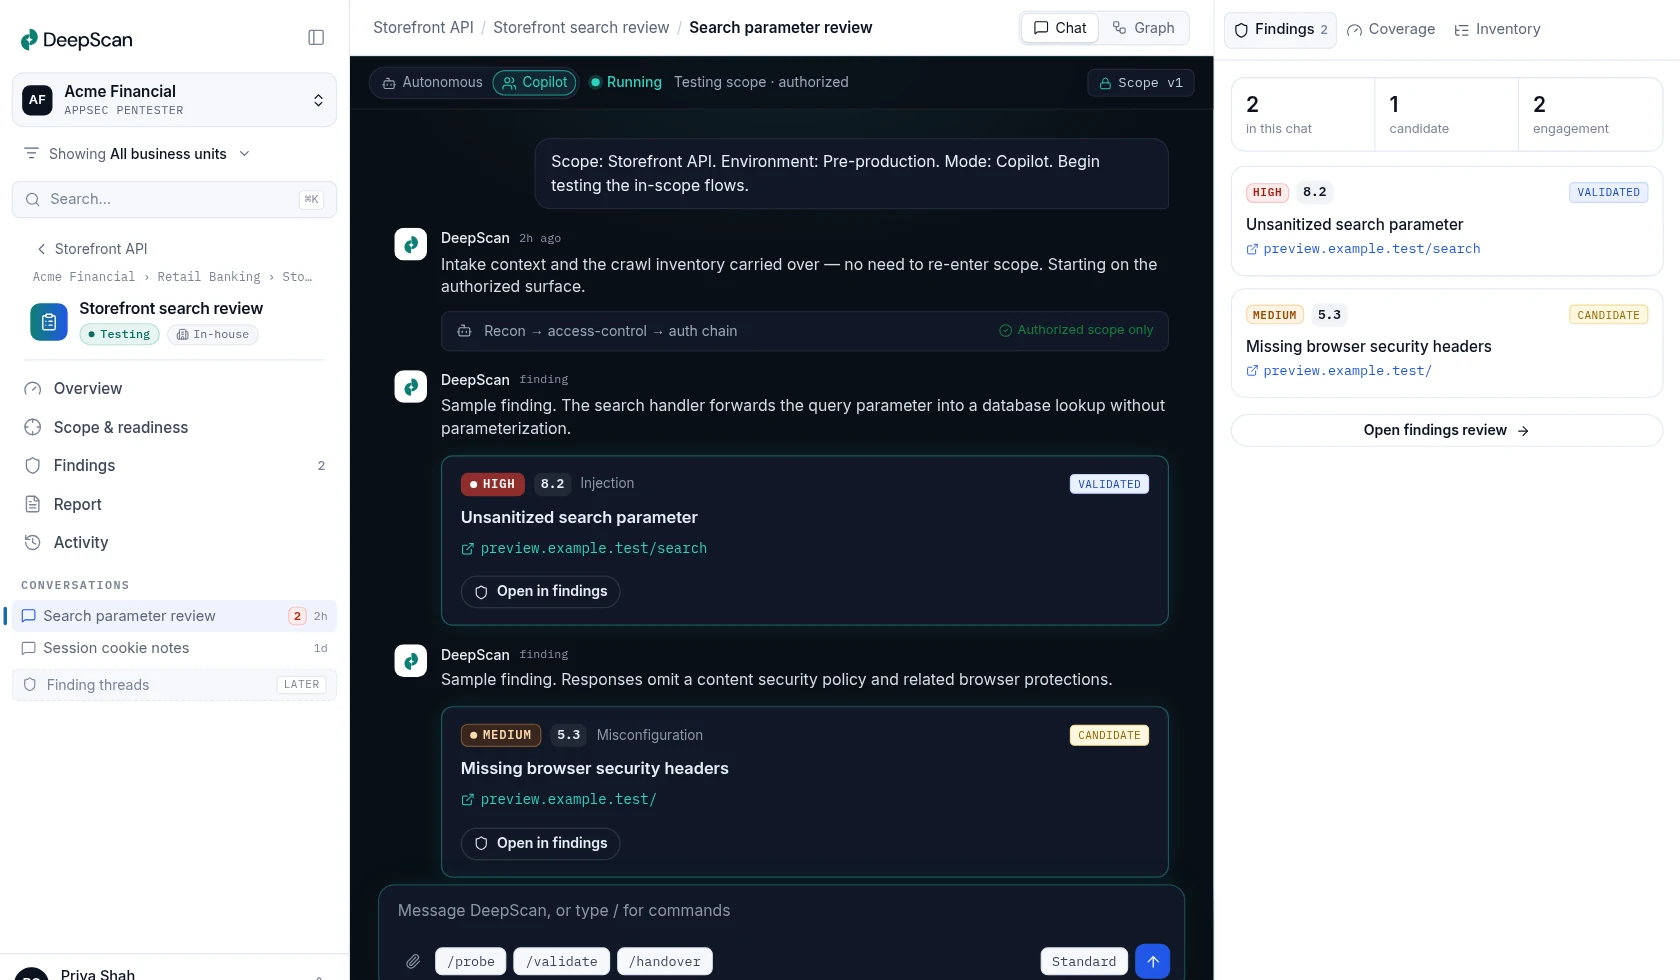
Introduce hypotheses, redirect agents, and deepen an investigation.
Controlled offensive workflow
Keep scope, testing decisions, and evidence connected.
Set objectives, targets, credentials, and safety boundaries.
Map applications, APIs, identities, workflows, and exposed paths.
Assign focused missions while preserving shared context.
Explore and chain weaknesses inside the approved scope.
Independently reproduce exploitability and business impact.
Document attack chains, tested objectives, evidence, and coverage gaps.
Operator workspace
Direct investigations alongside agents, with scope, attack paths, and evidence in view.
Governance and safety
Set the rules, steer execution, and review the evidence.
Questions
How DeepScan fits an existing offensive-security program.
No. DeepScan adds autonomous exploration and validation capacity while operators retain objectives, scope, approvals, and judgment.
Yes. In Copilot mode, pentesters prompt DeepScan to investigate hypotheses, redirect work, and pursue deeper attack paths as the surface becomes clearer.
Operators define the approved targets and rules of engagement, monitor agent activity, and pause or redirect testing. Expanding the target scope requires an approved update to the engagement.
Start with proof
Autonomous and Copilot on one controlled attack path.