Penetration Testing as a Service
Expert-led pentesting with DeepScan evidence.
Add specialist testers for a defined engagement. Scope, evidence and retest stay in DeepScan.
- Web
- APIs
- AI/LLM
- Cloud
- Mobile
- Compliance
Delivery assurance
A formal pentest when your team needs one.
DeepScan expert-led pentests are delivered through CyberImmune, a CREST Pathway Company.
Web Application Pentest
Expert-led testing for authentication, authorization, tenant boundaries, business logic, and high-impact web attack paths.
- Authentication and session management
- Authorization and tenant isolation
- Injection, SSRF, uploads, and workflow abuse
- Administrative and billing flows
- Reproducible evidence
- Engineering-ready remediation
- Formal scope and methodology
02API Pentest
Testing for authorization flaws, excessive exposure, abuse paths, replay, and chained impact across documented and observed APIs.
- Object and function-level authorization
- REST, GraphQL, and observed traffic coverage
- Token scope, replay, and abuse cases
- Sensitive data and multi-step chains
- Copy-ready request evidence
- Exploitability validation
- Retest-ready records
03AI Agent and LLM Pentest
Security testing for LLM applications, retrieval workflows, agent tools, sensitive context, and unsafe automation.
- Direct and indirect prompt injection
- Retrieval poisoning and boundary failures
- Tool permission abuse and excessive agency
- Sensitive information disclosure
- Multi-turn attack transcripts
- Tool and retrieval evidence
- Prioritized AI security findings
04Cloud and Mobile Assessment
Coordinated review of exposed cloud paths, mobile client behavior, backend APIs, identity controls, and secrets.
- Cloud identity and exposed storage
- Network and workload exposure
- Mobile storage, deep links, and API traffic
- Secrets and delivery-pipeline exposure
- Joined application and cloud evidence
- Risk-ranked fixes
- Reviewable methodology
05SOC 2, ISO 27001, and HIPAA Pentest
Pentest delivery structured to support assurance reviews, enterprise procurement, and customer security evidence needs.
- Testing aligned to the approved audit boundary
- Application and API validation
- Remediation and included retest workflow
- Executive and technical reporting
- Evidence that supports assurance workflows
- Reviewable findings and methodology
- Remediation and retest status
06Continuous Validation
Recurring testing and targeted retesting that keeps validated evidence current as applications and exposed paths change.
- Recurring validation across approved targets
- Regression retests after remediation
- Operator-triggered release validation
- Portfolio evidence review
- More current security proof
- Reduced stale-finding noise
- Reusable evidence history
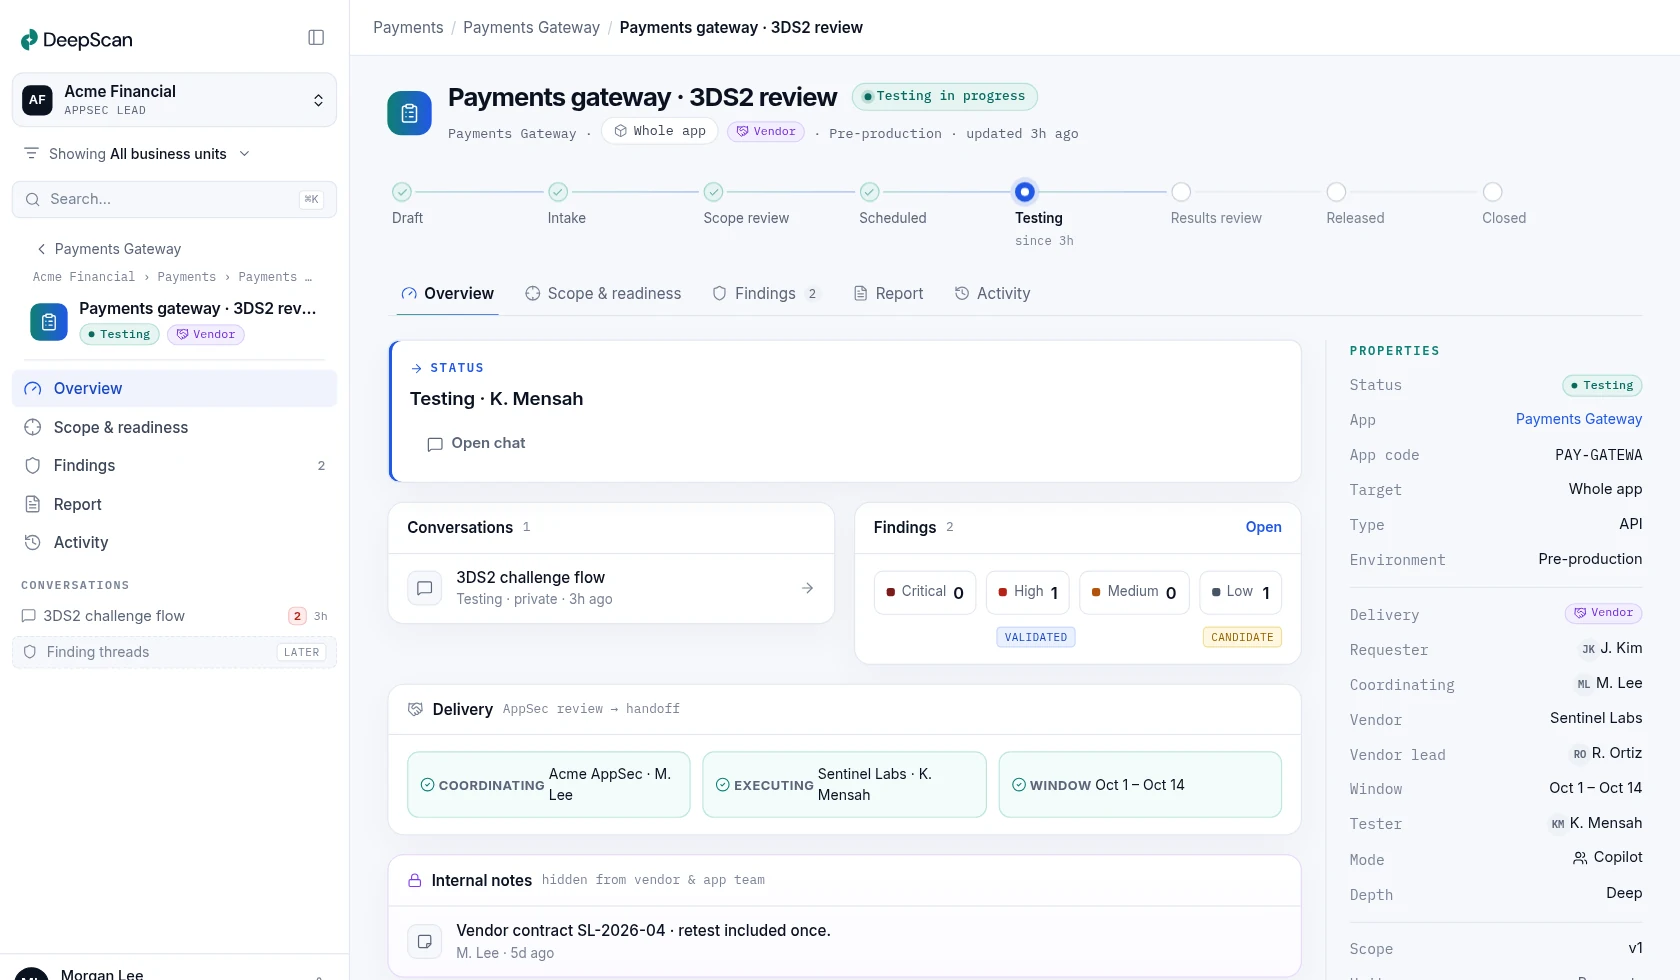
Vendor delivery
Experts test inside your engagement.
AppSec hands off. Testers work in a set access window. You release the results.
- Hand off
- Access window
- Review
- Release
deepscan · vendor delivery
Engagement workflow
Defined scope through retest.
One accountable sequence.
- 01
Scope
Define targets, objectives, credentials, exclusions, and delivery needs.
- 02
Test
Experts operate the DeepScan workflow inside the agreed rules of engagement.
- 03
Validate
Confirm exploitability and review evidence quality before reporting.
- 04
Report and retest
Deliver findings, remediation context, and the agreed retest workflow.
Choose the operating model
Platform autonomy or expert-led delivery.
Same evidence. Your choice of operator.
| Capability | Traditional approach | DeepScan |
|---|
| Operation | Your team runs DeepScan directly. | CyberImmune experts lead the agreed engagement. |
|---|
| Cadence | On demand or continuous. | Defined scope, timeline, and retest. |
|---|
| Output | Live findings and evidence workflow. | Formal report plus remediation and retest status. |
|---|
Questions
Scoping an expert-led pentest.
The essentials before an engagement begins.
Who delivers the pentest?
DeepScan expert-led pentests are delivered through CyberImmune, a CREST Pathway Company.
What does the report include?
The agreed scope, methodology, findings, evidence, impact, remediation guidance, and retest status.
Can we continue testing after the engagement?
Yes. Teams can move into recurring validation or operate the DeepScan platform directly.
Start with proof
Scope the right pentest.
Tell us what needs testing and when.