App teams ask once.
- Request
- Light crawl
- Submit
Platform
Requesters, your AppSec team and vendors run every pentest in one engagement. Agents test. Your experts steer and release.
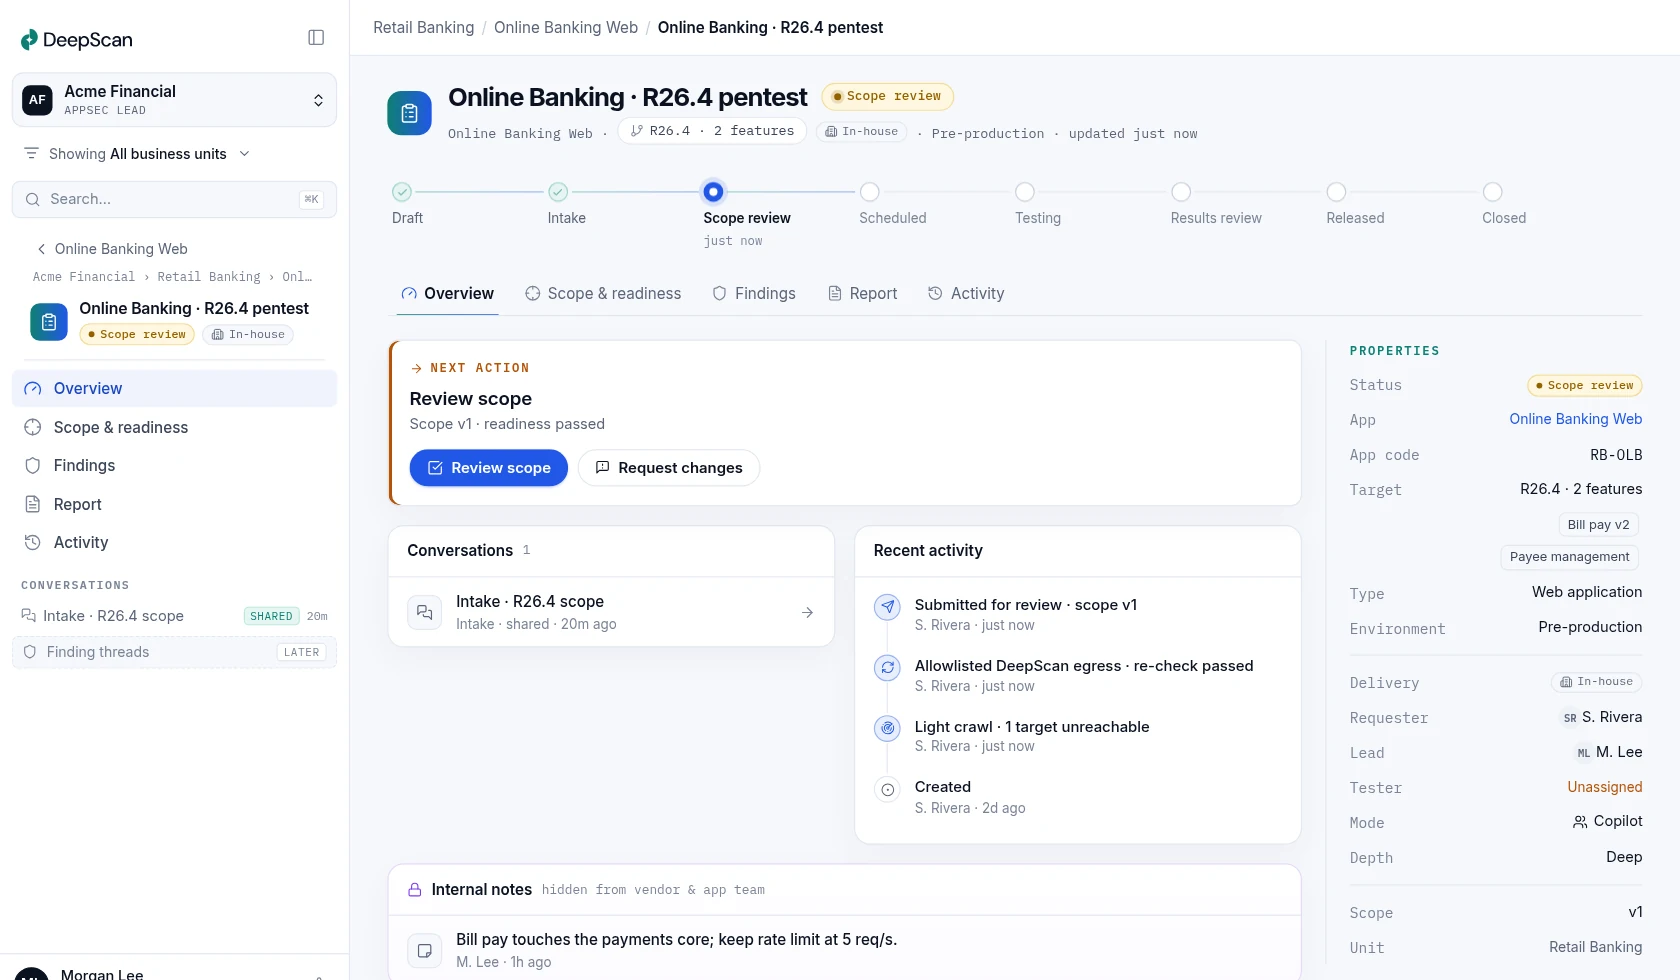
Engagement lifecycle
Request, scope, test, release and retest in one record.
Live testing
Run Autonomous, or switch to Copilot to push a hypothesis.
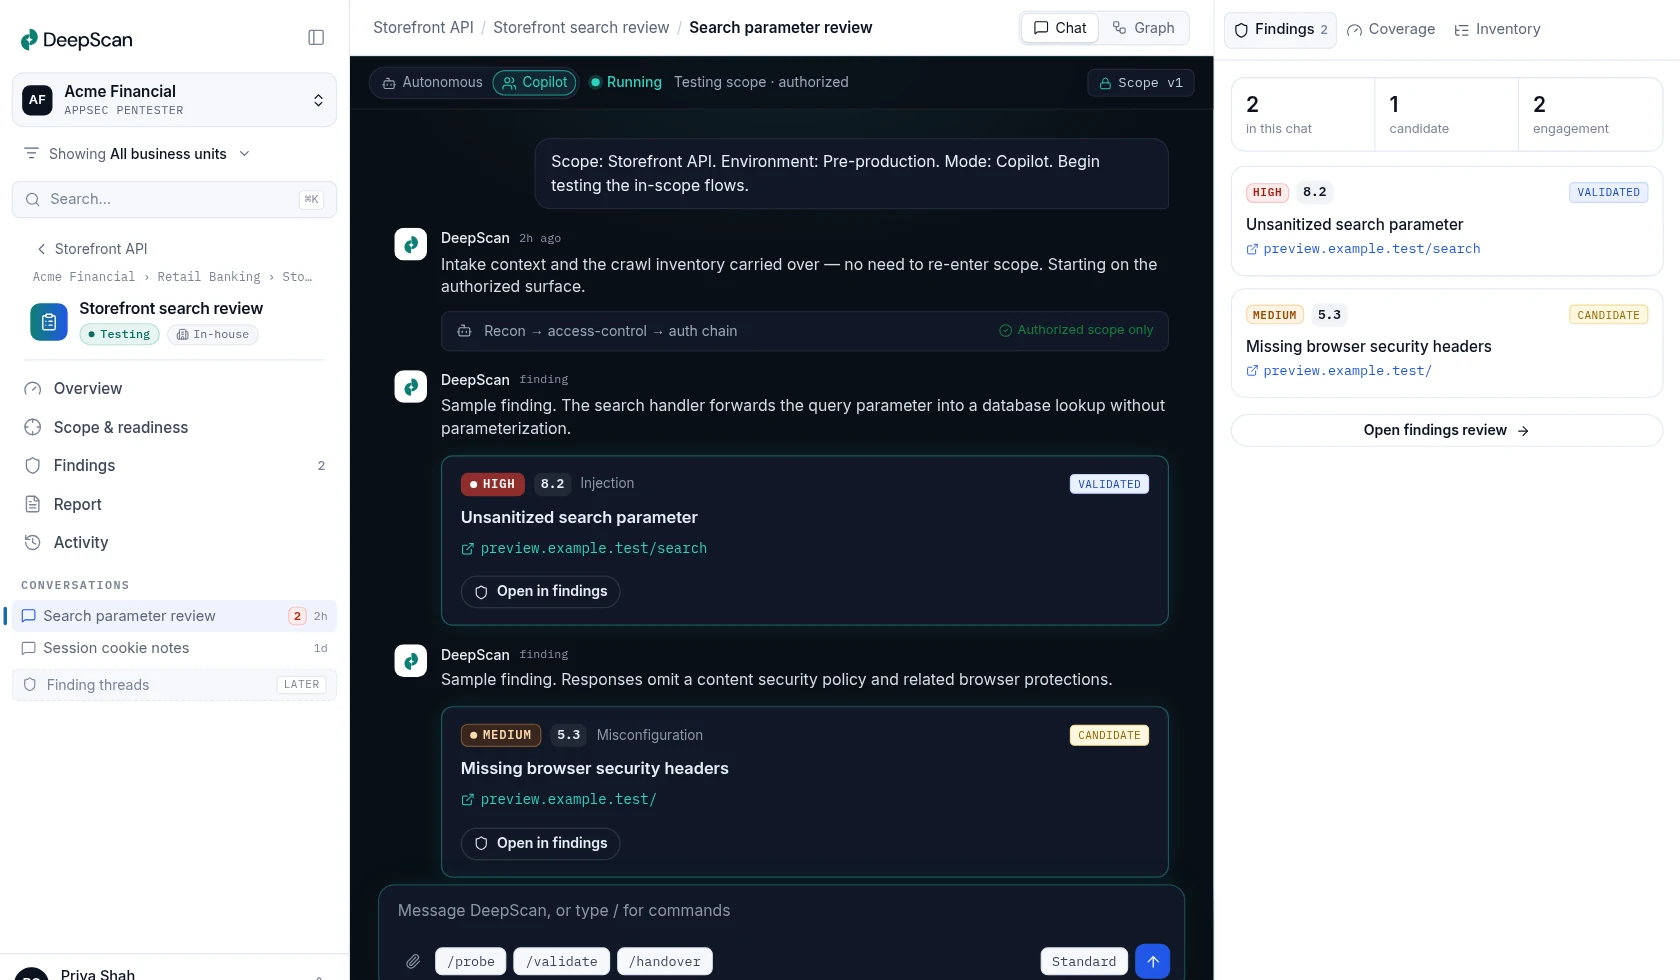
Testing engine
Specialist agents share one attack context.
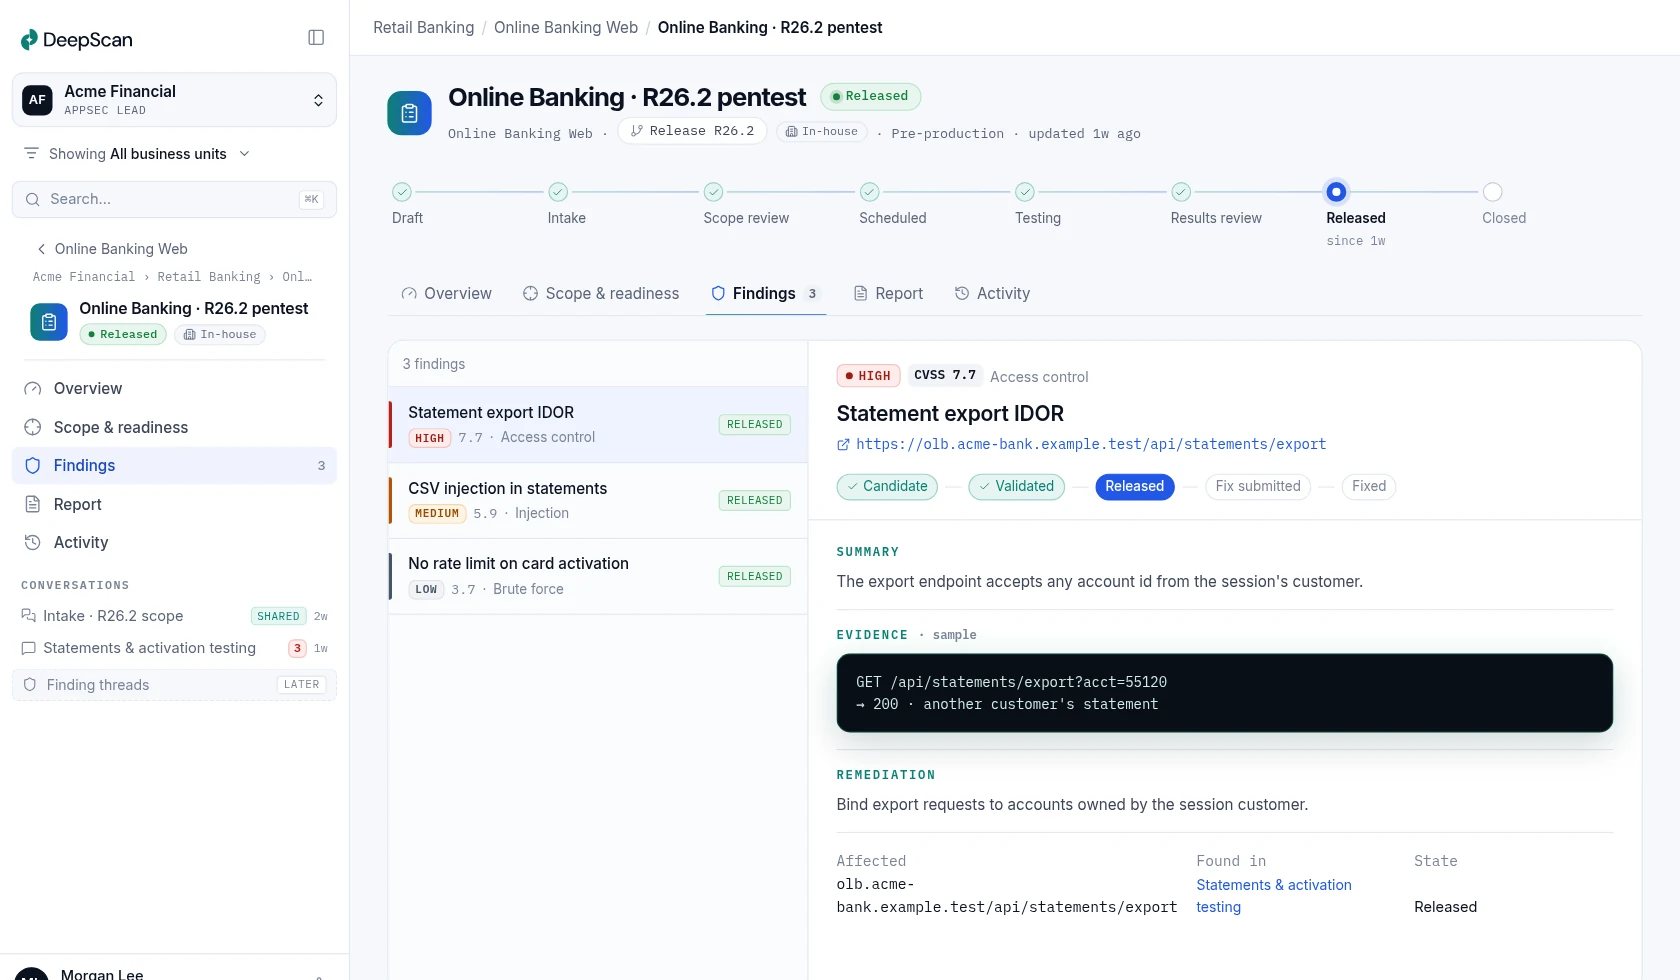
Evidence
AppSec reviews, releases and tracks retest in the same engagement.
Governance and safety
Autonomy stays inside approved scope.
Delivery
DeepScan expert-led pentests are delivered through CyberImmune, a CREST Pathway Company.
Teams can provide target URLs, credentials, API specifications, documentation, architecture notes, and explicit testing objectives.
Yes. Readiness checks prepare the engagement; after explicit approval, DeepScan autonomously maps and tests the target while pentesters can steer deeper work through chat.
A candidate is reproduced against the approved target and attached to evidence before it is treated as a confirmed finding.
Yes. Teams can operate the platform directly or request a CyberImmune-delivered expert engagement.
Start with proof
A walkthrough for your AppSec or Red Team workflow.